
01
Exposed public services
Untracked websites, VPN, NAS, remote access, and management interfaces leave unnecessary entry points.

SERVER PLUS SECURITY SERVICE
Website scanning, external IP review, CVE risk inventory, and remediation retesting.
Identify exposure across public services, servers, and network equipment, then deliver risk ranking and actionable remediation guidance.
ENTERPRISE SECURITY REALITY
The common problem is not a lack of tools but an unclear scope, priority, and remediation owner.
01
Untracked websites, VPN, NAS, remote access, and management interfaces leave unnecessary entry points.
02
Untracked firewall, switch, server, and package versions can retain known CVEs.
03
Long tool reports are less useful than a prioritized, executable plan for high-risk findings.
04
Customer audits, cyber insurance, and supply-chain requirements need documented risk status and improvement records.
SCAN SCOPE
Confirm authorized scope before scanning to avoid affecting unauthorized assets or production services.
External IP and domains
Website and web vulnerability scanning
Web services and common weaknesses
OWASP risk categories
VPN, firewall, and NAS
Windows and Linux servers
SSL/TLS certificates and encryption settings
CVEs, misconfiguration, and high-risk services
SCANNING SERVICES
The scope can be planned around assets and includes web scanning, external IP review, CVE scanning, and security assessment reporting.
01
Review web services, SSL/TLS, configuration issues, sensitive-data exposure, and OWASP risk areas.
02
Inventory public IPs, domains, VPN, NAS, remote access, and management interfaces.
03
Compare known vulnerabilities against server, network-device, and service versions, then prioritize high-risk findings.
04
Turn scan output into an enterprise improvement list, with retesting and audit evidence support.
SCAN BY SCENARIO
01
Review remote-access exposure, versions, SSL/TLS, and known CVEs.
02
Review SSL VPN, public management exposure, firmware, and firewall risk.
03
Review remote services, administration exposure, and identifiable version risk.
04
Review public services before a website, API, VPN, or system enters production.
05
Confirm that high-risk remediation is effective and exposure is reduced.
06
See how risk, assets, remediation ownership, and retesting should be presented.
SERVER PLUS × REDMARK
Choose a managed enterprise assessment, automated website scanning, or combine both according to asset scope and operating model.
SERVER PLUS MANAGED ASSESSMENT
For websites, external IPs, VPNs, firewalls, NAS, and servers, including scope confirmation, risk ranking, remediation guidance, and retesting.
REDMARK AUTOMATED PLATFORM
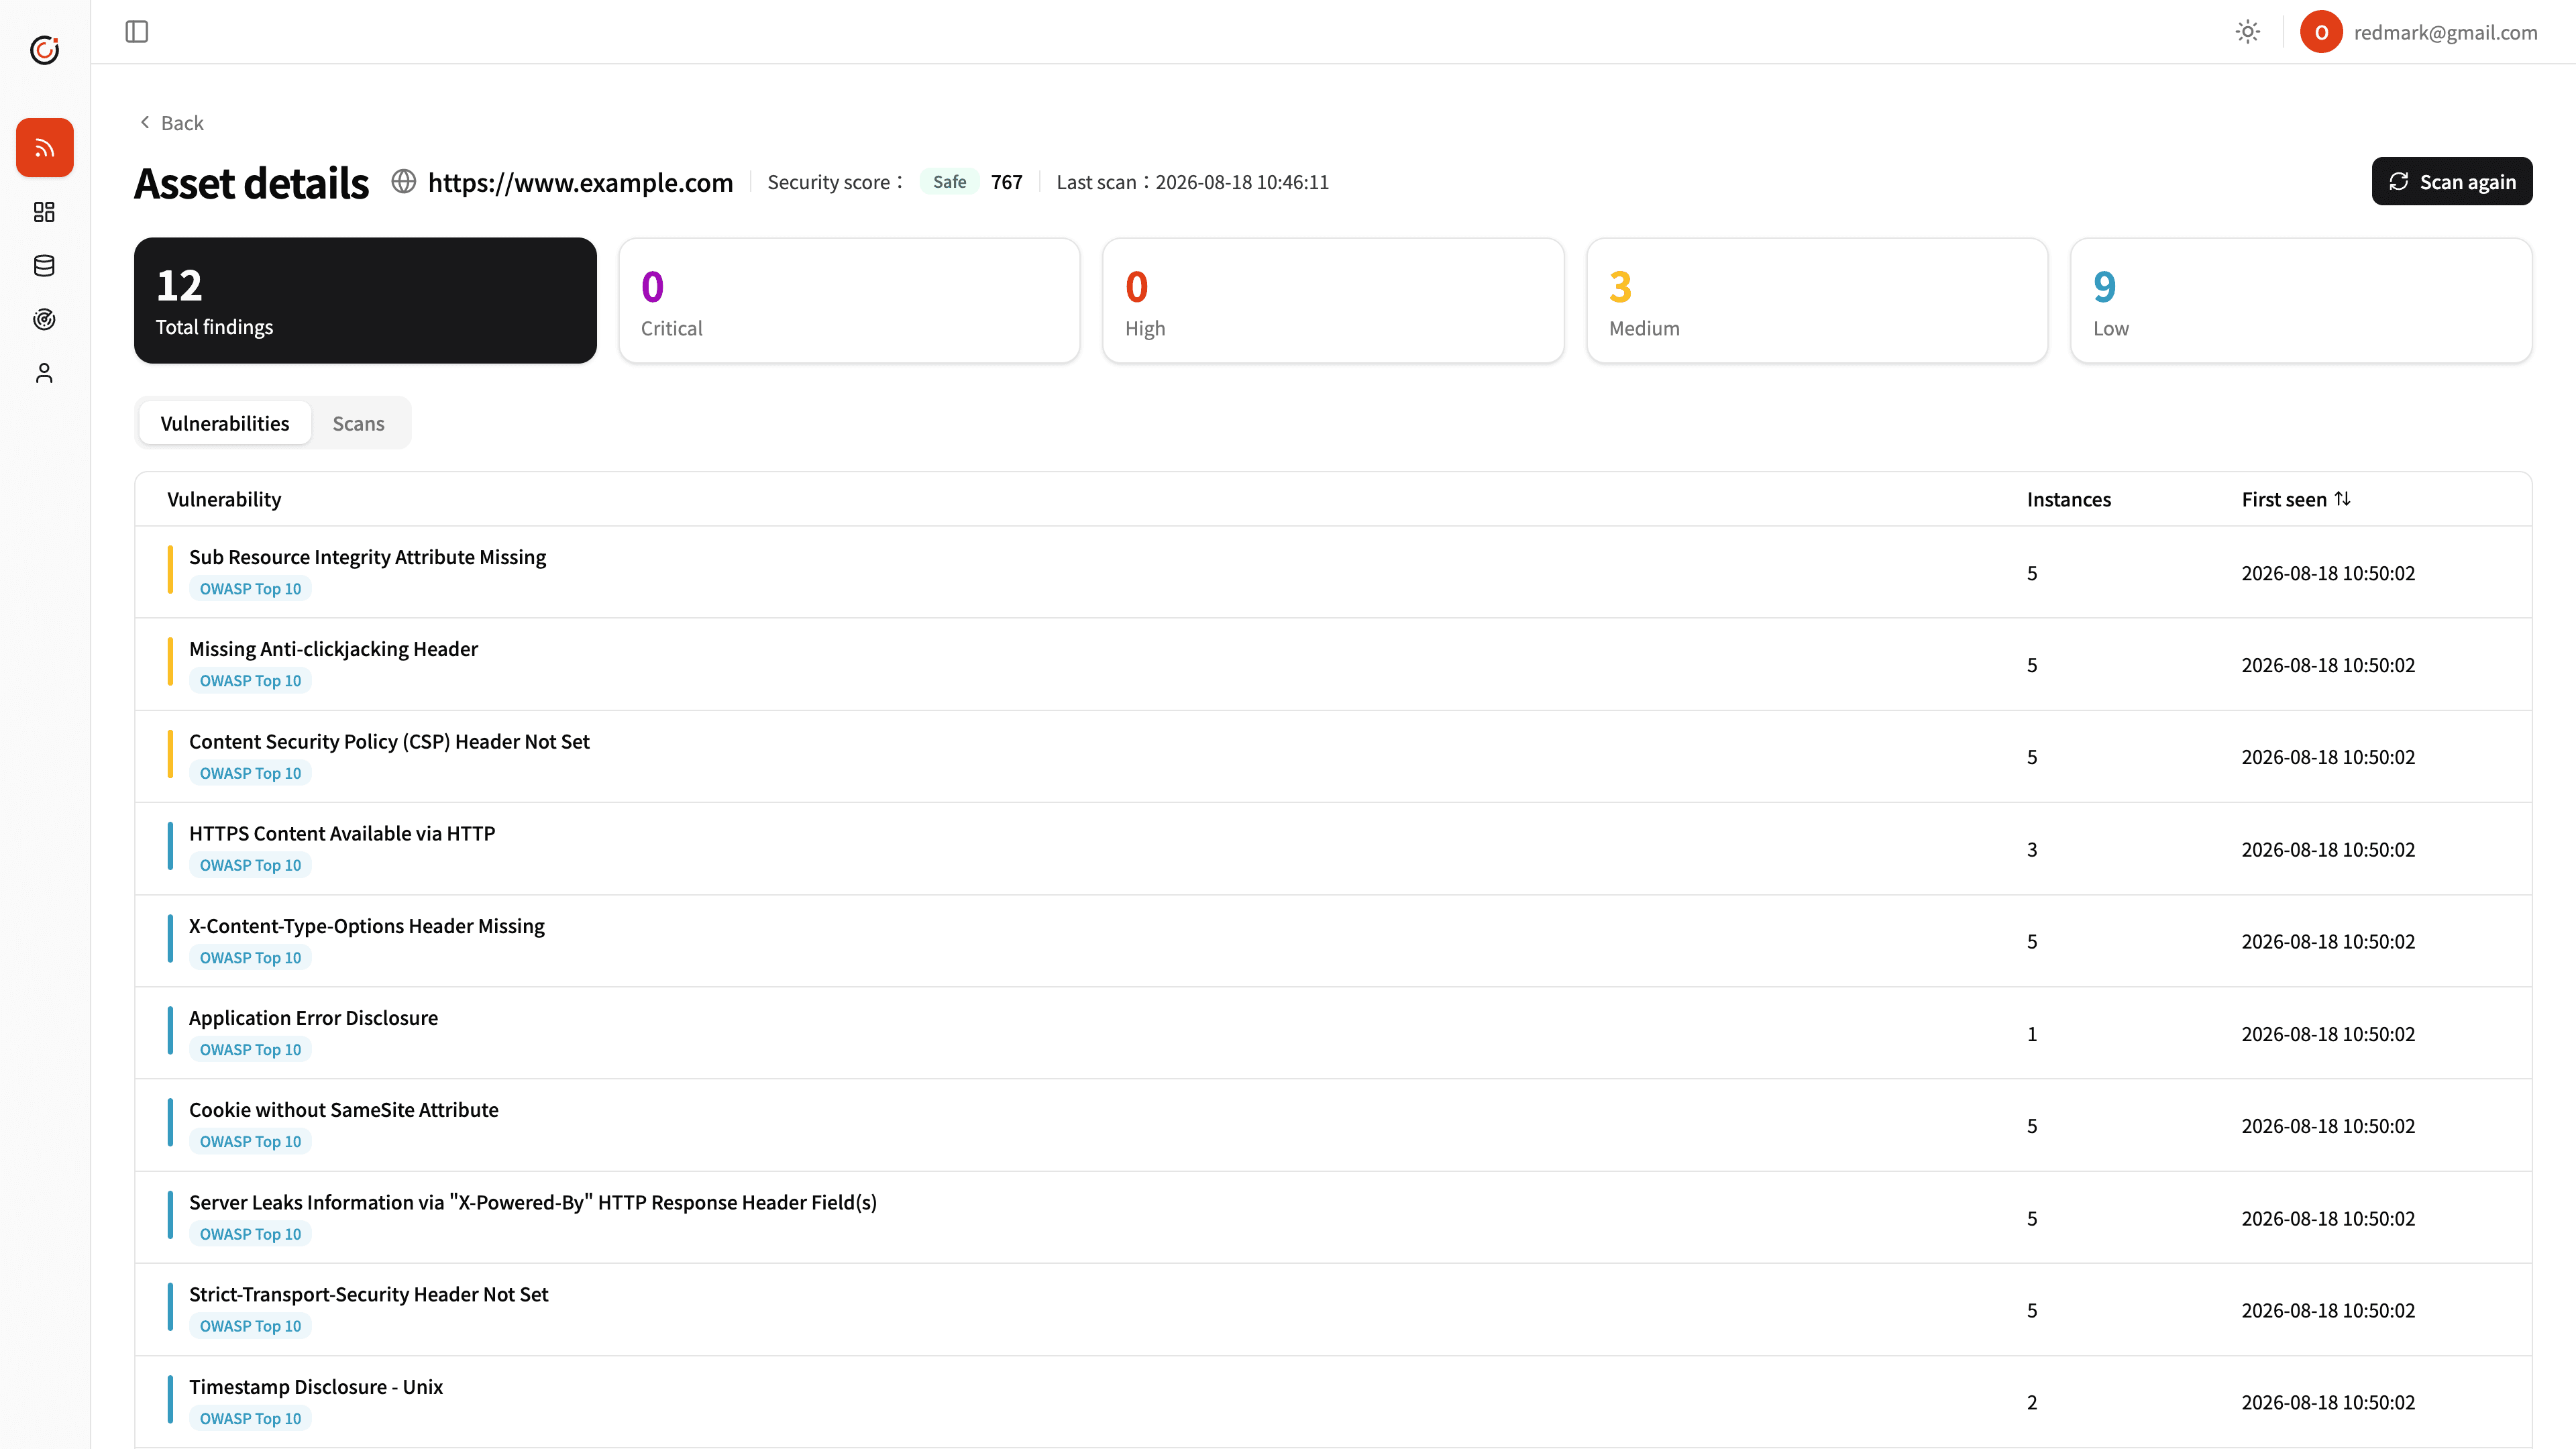
For teams that want to create website scan tasks, schedule recurring checks, and manage findings, evidence, and remediation direction centrally.
DELIVERABLES
Reports are organized for both management and IT teams, prioritizing risks that actually affect services.
Vulnerability scan report
Finding summary and risk classification
Affected services and impact description
High-risk remediation priorities
Optional post-remediation retest
SERVICE PROCESS
Authorization is confirmed first, and scans can avoid business peaks or critical maintenance windows.
Confirm scope
Confirm authorization
Run scan
Deliver report
Provide remediation guidance
FAQ
01
Scanning focuses on known vulnerabilities, misconfiguration, and high-risk services; an assessment further organizes assets, risk, remediation order, and improvement records.
02
Typical checks include web-service configuration, SSL/TLS, known CVEs, sensitive-information exposure, and OWASP risk areas within the authorized asset scope.
03
Yes. External IP scanning is suitable for websites, VPN, firewalls, NAS, remote access, and public management interfaces.
04
Yes. A retest can confirm whether high-risk findings have been reduced or closed after remediation.
EXECUTION PRINCIPLE
Enterprise teams need to know which findings are externally exposed, affect production services, or can be corrected quickly across websites, external IPs, VPN, firewalls, NAS, servers, and cloud hosts.
Server Plus confirms scope, timing, asset types, and exclusions before organizing findings, risk levels, affected services, remediation guidance, and retesting. New refurbished servers or network equipment can be reviewed for exposure before production use.
VULNERABILITY-SCAN ASSESSMENT
Provide IPs, domains, device types, and the desired scan window for scope and quotation assessment.
Only need automated recurring website scanning? Open RedMark