SERVER PLUS INSIGHTS
Your Firewall Is Still Running. Is Your Uplink Already Saturated? Server Plus Enterprise DDoS Protection
A working firewall does not guarantee that customers can reach your services. When a volumetric DDoS attack saturates the upstream link, congestion can block legitimate packets before they reach your equipment. Server Plus enterprise L3/L4 Anti-DDoS extends protection upstream, combining global edge mitigation with delivery by a Taiwan-based team to plan connectivity, protection and routing together.
2026-10-21 · Server Plus
Server Plus L3/L4 Anti-DDoS combines Cloudflare Magic Transit, Taiwan-based technical support, Chief Telecom data-center or FTTB delivery, and 95th-percentile clean-bandwidth billing. Submit your ASN, IPv4 prefixes and normal traffic for an assessment.
Video overview
The equipment is running, but the bottleneck may be upstream
Enterprise firewalls enforce access control, connection management and security policies. When attack traffic exceeds access-link capacity, legitimate connections may fail even if the firewall has processing headroom. Upgrading on-premises equipment alone may therefore not resolve outages caused by volumetric DDoS attacks.
For websites, APIs, VPNs, hosted servers and public-facing data-center services, assessments must consider more than firewall performance: where is attack traffic mitigated, and how does legitimate traffic return to the enterprise network?
Cloudflare Magic Transit: detection and mitigation at the global edge
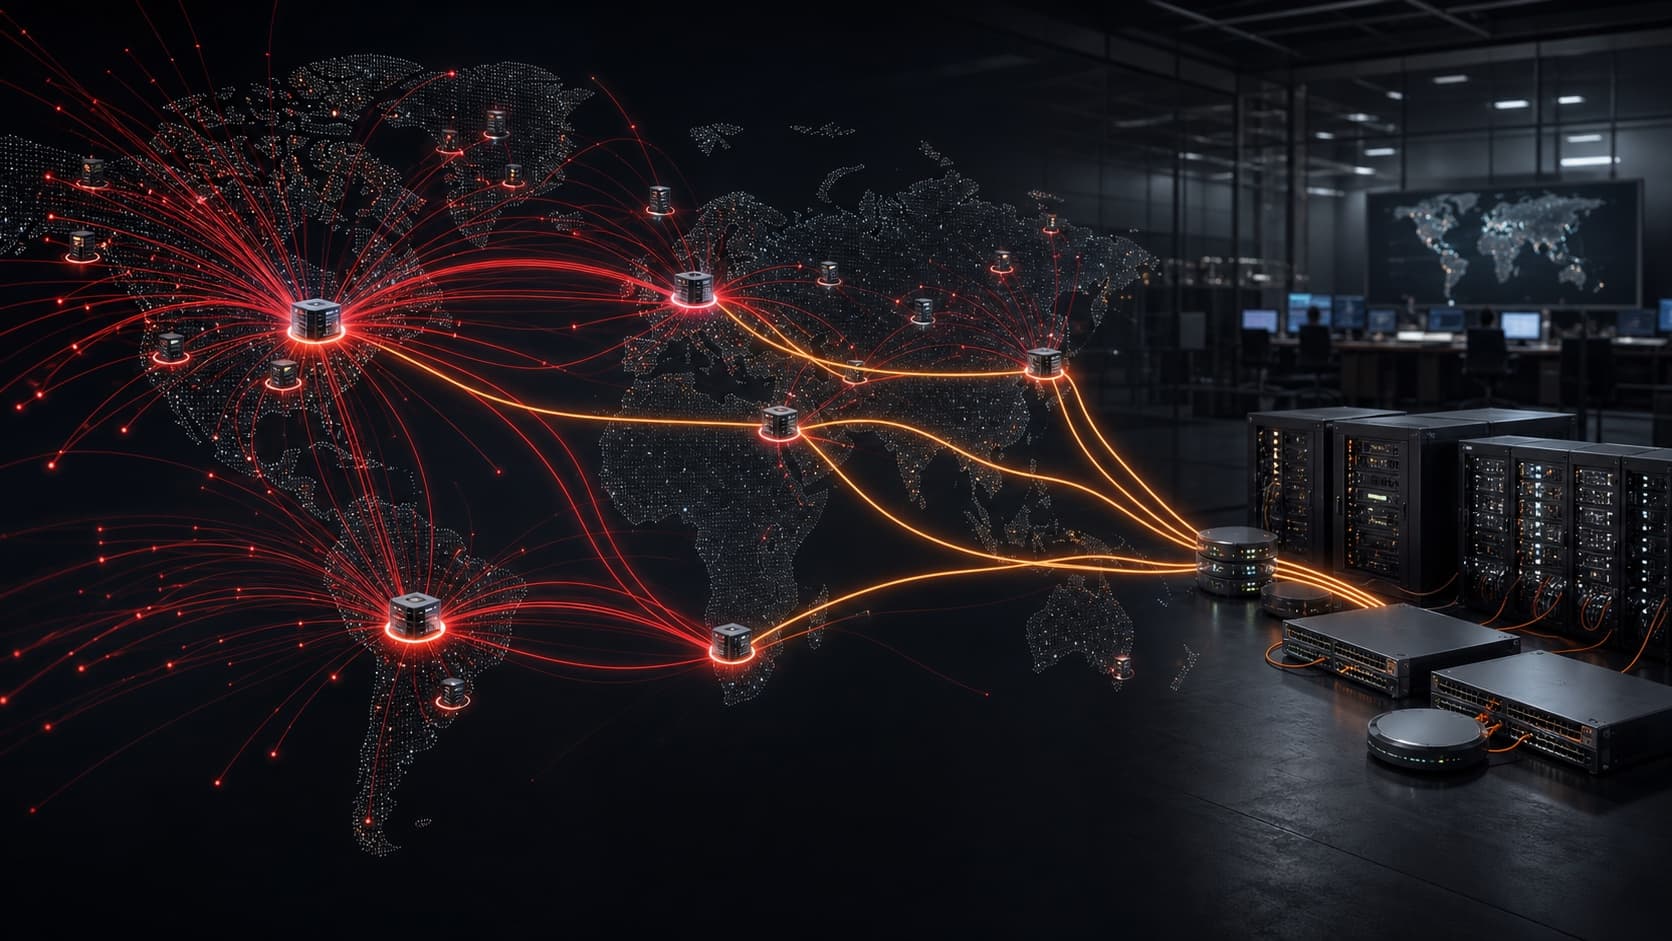
Server Plus uses a Cloudflare® Magic Transit™ protection architecture. Traffic for protected prefixes enters the global Anycast network, where L3/L4 DDoS attacks are identified and mitigated. Legitimate traffic is then delivered through the Server Plus network to the enterprise data center or office.
Global mitigation and customer delivery are separate stages. Cloudflare provides the global protection architecture; the Server Plus team in Taiwan handles requirements, routing design, cutover validation and incident assistance to integrate the service with the existing environment.
Information security management and a Taiwan-based technical team
Server Plus has achieved ISO/IEC 27001:2022 information security management system certification and provides Taiwan-based technical support for enterprise deployment and operations.
Enterprises can discuss protected services and prefixes, BGP, delivery circuits and cutover arrangements directly with the local team. A designated contact also assists with incidents, extending support beyond plan specifications.
Direct ports and multi-location delivery for data centers and offices
Select delivery based on location, legitimate traffic and redundancy requirements. Server Plus provides delivery through its own ports and evaluates protection alongside actual access conditions.
- Chief Telecom data center: direct 10G / 25G / 40G / 100G handoff according to the selected plan.
- Chunghwa Telecom FTTB: assessment is available for Shield Lite and Shield Pro, subject to installation address, circuit conditions and requirements.
- Taipei / Tokyo / Hong Kong: clean-traffic delivery points and redundancy are planned by service tier; not every plan includes all three locations.
- Port speed and included clean bandwidth are confirmed separately. A 10G port does not imply a 10Gbps legitimate-traffic allowance.
95th-percentile clean bandwidth excludes blocked attack traffic
Clean bandwidth is billed at the 95th percentile. Attack traffic identified and blocked by the protection platform is excluded from clean-bandwidth usage. Legitimate traffic delivered after mitigation is accounted for under the selected plan and agreement.
Legitimate traffic above the included bandwidth is charged at the agreed overage rate. Delivery ports, data-center cross-connects and access circuits are quoted separately so enterprises can distinguish protection, bandwidth and access costs.
Submit your ASN, IPv4 prefixes and normal traffic for an assessment
For data-center services, enterprise VPNs, public-facing platforms or fixed-prefix protection, send the following information through LINE. Server Plus will help plan protection capacity, routing and delivery.
- ASN and IPv4 prefixes to protect.
- Typical, 95th-percentile and peak legitimate traffic.
- Data-center location or office installation address.
- Current upstream providers, BGP design and redundancy requirements.
- Target go-live date and whether an attack is in progress.
FAQ
Why plan upstream DDoS protection if we already have a firewall?
A firewall processes traffic that reaches it. If the upstream link is saturated first, legitimate connections may never reach the device. Upstream scrubbing complements enterprise security policies in a layered design.
Does blocked attack traffic increase clean-bandwidth charges?
Traffic identified and blocked by the platform is excluded from clean bandwidth. Legitimate traffic delivered after mitigation and any overage are billed under the plan and agreement.
How do we start an assessment?
Send your ASN, IPv4 prefixes, normal traffic and delivery location through LINE. The Taiwan-based team will help confirm routing, ports, circuits and an appropriate plan.