

SERVER PLUS INSIGHTS
RedMark Automated Vulnerability Scanning Platform Launch: Build a Continuous Website Security Process
Websites change continuously. Vulnerability testing should not happen only before launch or after an incident. RedMark brings website scanning, scheduling, risk assessment, and reporting into one platform so teams can operate a repeatable security process.
2026-08-23 · Server Plus
RedMark is a SaaS platform for automated website vulnerability scanning and risk management. It brings on-demand scanning, scheduled checks, risk classification, remediation guidance, and report generation into one workflow so teams can make security testing continuous.
REDMARK PLATFORM
Start continuous website vulnerability scanning
Use RedMark to create website scan tasks, schedule recurring checks, review findings, and generate actionable reports from one platform.
Website Risk Does Not Wait for the Next Manual Review
Websites, administration portals, and APIs change with new features, package updates, configuration changes, and third-party integrations. When scanning is only scheduled for project handover, annual audits, or after an incident, new exposure can remain between reviews.
Many teams understand the need for security testing but struggle to make it routine because of deployment effort, operational complexity, consultant cost, and the time required to consolidate results manually.
RedMark: Automated Website Scanning SaaS
RedMark combines website vulnerability scanning, scheduled checks, findings review, and report generation in one SaaS platform. Teams can create scans for their assets, set an execution cadence, and review findings and remediation direction from one place.
The platform focuses on continuous assessment of website assets. It is designed for teams that want to lower the operational threshold for recurring scanning, maintain visibility of risk, and use the same findings across IT, development, and security functions.
- Create website scan tasks on demand
- Set automated recurring checks around operations needs
- Review findings, severity, and affected locations centrally
- Use OWASP categories, evidence, and remediation direction for triage
- Generate deliverable vulnerability scan reports
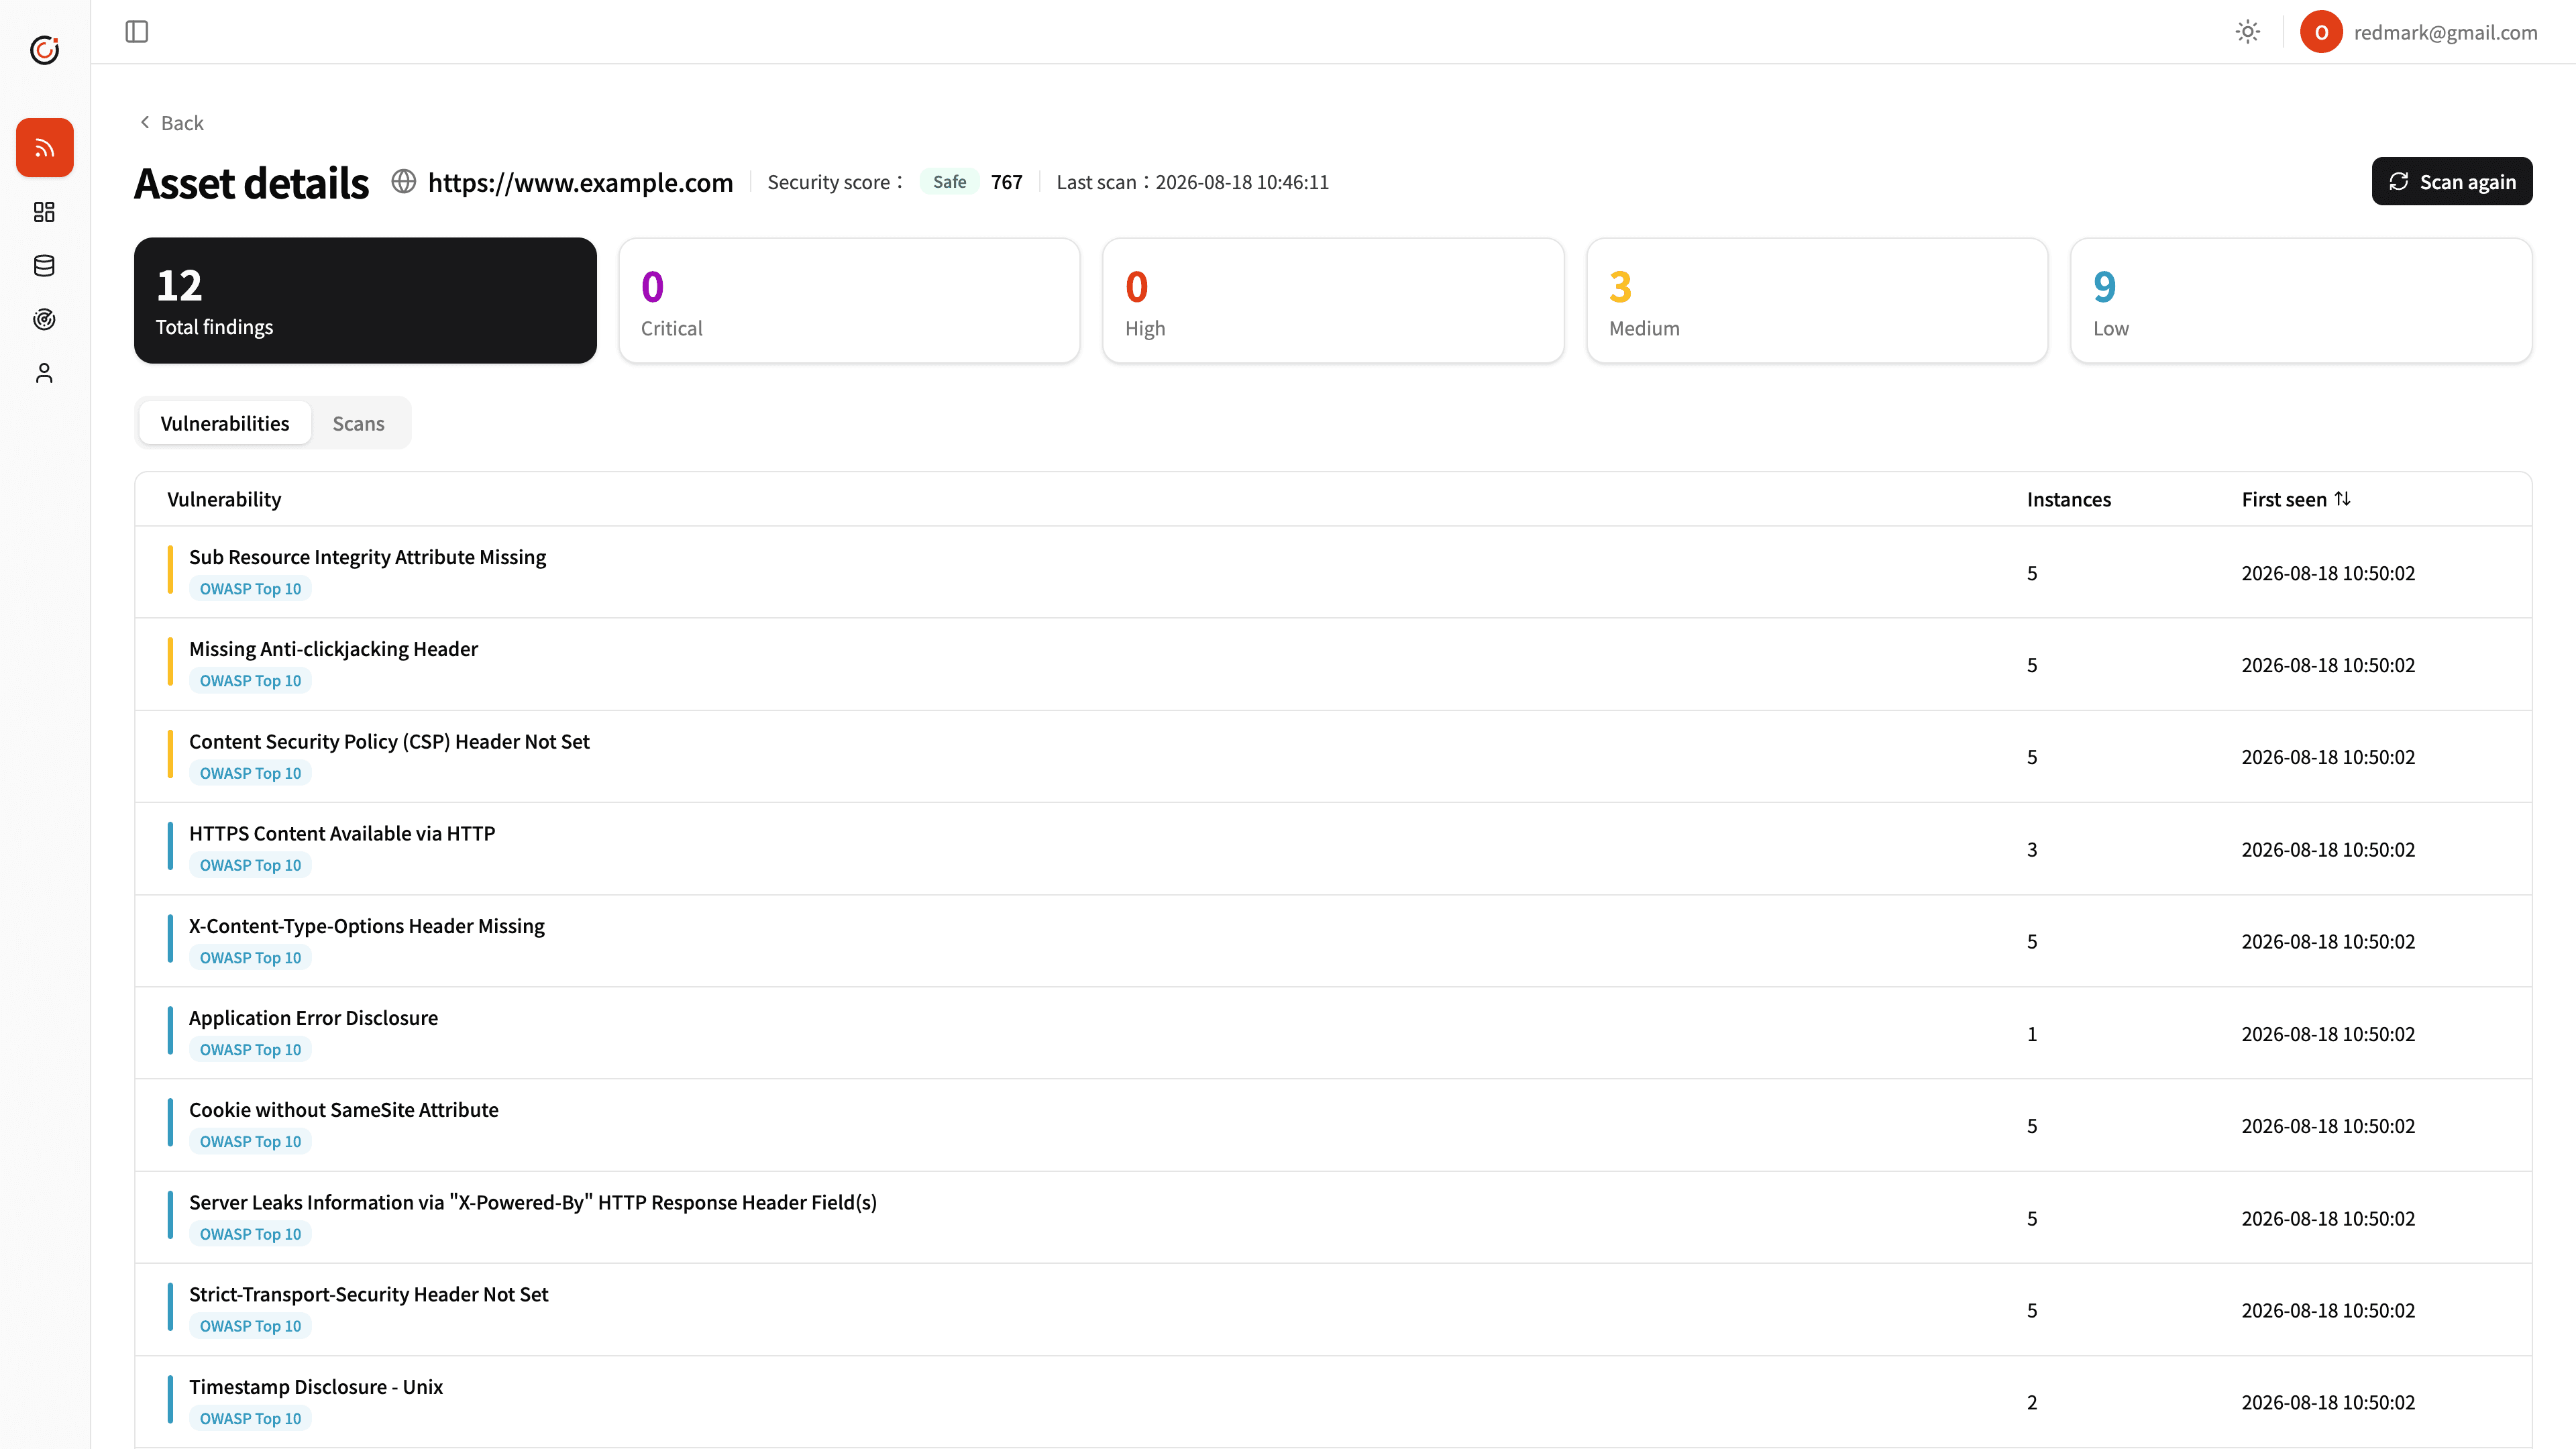
The Value of Scanning Is Continuous Follow-Through
A single scan reveals the current state; recurring scans help teams reassess assets after site changes, service adjustments, or newly disclosed vulnerabilities. Scheduling and centralized management reduce dependence on manual reminders and repeated environment preparation.
Results also need to become actionable work. Severity, affected location, evidence, and remediation guidance help development, operations, and management prioritize on the same basis.
How Server Plus and RedMark Fit Together
Server Plus continues to provide enterprise vulnerability scanning and security assessment services for engagements that need authorized scope definition and assessment across external IPs, VPNs, firewalls, NAS, servers, or multiple enterprise assets.
RedMark provides an automated SaaS workflow focused on website assets, suited to teams that want to operate recurring website scans, scheduled checks, and report management themselves. The two services can be planned together according to asset scope, execution frequency, and internal ownership rather than treated as replacements.
- Continuous website scanning and internal day-to-day tracking: RedMark
- Authorized multi-asset assessment and enterprise security review: Server Plus
- Post-remediation validation and delivery evidence: scope based on the affected assets
Confirm Asset Authorization and Service Capacity First
Only scan assets for which you have lawful authorization. Before a scan, confirm control of the domain, website, API, or other target service, then choose scope and frequency around service capacity, maintenance windows, and existing safeguards.
FAQ
Which teams is RedMark designed for?
RedMark is suitable for IT, development, and security teams that want recurring website vulnerability scanning, periodic checks, risk tracking, and reporting.
How does RedMark differ from Server Plus vulnerability scanning services?
RedMark is an automated SaaS platform centered on website assets. Server Plus provides enterprise scanning and security assessment services that can cover authorized external IPs, VPNs, firewalls, NAS, servers, and multi-asset requirements.
Can I scan another website without authorization?
No. Every scan requires lawful authorization from the owner of the target asset and must be planned around the service capacity and maintenance arrangements.